TL;DR

Prime made for students and young adults
- Fast, free delivery for dorm and study essentials
- Prime Video and Amazon Music included
- Member-only deals
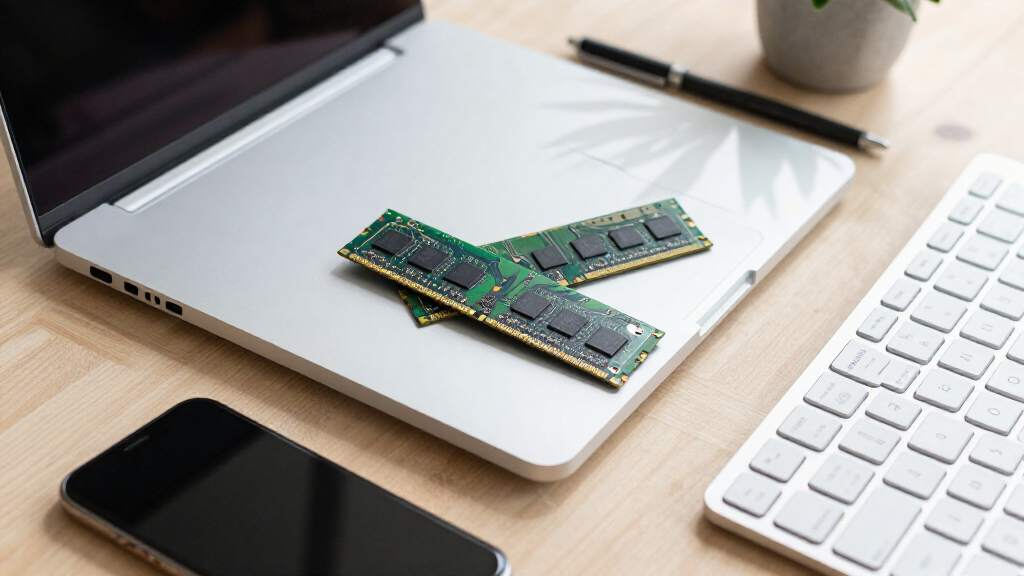
Researchers have clarified the mechanisms behind DRAM read disturbance phenomena, including RowHammer and RowPress. These effects pose security risks and are the focus of ongoing investigations to improve memory reliability.
Recent research has advanced understanding of DRAM read disturbance phenomena, specifically RowHammer and RowPress. These effects, which can cause data corruption through repeated memory access, are recognized as security vulnerabilities and hardware reliability issues. The new findings clarify the mechanisms behind these phenomena, aiding efforts to develop effective mitigation strategies.
RowHammer was first identified in 2014 as a security vulnerability where repeatedly accessing a specific row in DRAM can cause bit flips in adjacent rows. RowPress, a related but distinct phenomenon, involves disturbance effects that can alter data in the same or nearby rows through different access patterns. Recent academic publications have provided detailed models explaining how these effects occur at the physical and circuit levels, confirming that the disturbance is caused by charge leakage and interference between memory cells.
Industry experts and researchers have emphasized that these phenomena are not merely theoretical but have been demonstrated in various DRAM modules, including commercial products. However, the severity and frequency of bit flips depend on specific hardware designs, manufacturing processes, and usage patterns. While mitigation techniques such as error-correcting codes (ECC) and refresh rate adjustments exist, the new insights aim to inform more robust hardware and software defenses.
Implications for Memory Security and Reliability
The clarification of RowHammer and RowPress mechanisms underscores the importance of addressing these effects in both hardware design and cybersecurity. As DRAM remains a core component of computing systems, vulnerabilities can lead to data corruption, system crashes, or security breaches. The research highlights the need for ongoing development of mitigation strategies, including hardware improvements and software patches, to protect sensitive data and maintain system integrity.
As an affiliate, we earn on qualifying purchases.
Recent Advances in Understanding DRAM Disturbance Effects
Since the initial discovery of RowHammer in 2014, researchers have studied various ways to exploit and mitigate the effect. Early work demonstrated that repeatedly accessing a row could induce bit flips in adjacent rows, raising security concerns. Over the years, new variants like RowPress have been identified, which involve different access patterns and physical effects. Recent publications have utilized advanced modeling and physical analysis to better understand the root causes, confirming that charge leakage and cell interference are primary factors. Industry has also begun integrating these insights into hardware design considerations, but comprehensive solutions are still under development.
As an affiliate, we earn on qualifying purchases.
Remaining Questions About Long-Term Mitigation Strategies
It is still unclear how different DRAM manufacturing processes influence the severity of RowHammer and RowPress effects. The effectiveness of proposed hardware fixes and software patches in real-world deployments remains under evaluation. Researchers continue to investigate whether new memory technologies can inherently prevent these disturbance effects, but definitive solutions are not yet available.
As an affiliate, we earn on qualifying purchases.
Next Steps in Research and Hardware Development
Future research will focus on refining physical models of disturbance effects and testing new memory architectures designed to resist such phenomena. Industry efforts are expected to accelerate the integration of these insights into next-generation DRAM chips. Additionally, regulatory and security communities will likely develop standards and best practices for mitigating risks associated with RowHammer and RowPress in critical systems.
DRAM security vulnerability mitigation
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is RowHammer in DRAM?
RowHammer is a phenomenon where repeatedly accessing a specific row in DRAM can cause unintended bit flips in adjacent rows, potentially leading to data corruption and security vulnerabilities.
How does RowPress differ from RowHammer?
RowPress involves disturbance effects that can alter data within the same or nearby rows through different access patterns, with physical mechanisms similar to but distinct from RowHammer.
Are these effects common in all DRAM modules?
They have been demonstrated in various DRAM modules, including commercial products, but their severity depends on hardware design, manufacturing, and usage patterns.
What can be done to prevent these disturbances?
Mitigation strategies include error-correcting codes, increased refresh rates, and hardware redesigns aimed at reducing cell interference. Ongoing research aims to develop more robust solutions.
Why do these phenomena matter for cybersecurity?
Because they can be exploited to induce errors or manipulate data, posing security risks such as privilege escalation or data breaches in sensitive systems.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.